Cybersecurity
High-Severity Chrome V8 Bug CVE-2026-126910 Raises Exploit Concerns
Test code for CVE-2026-126910, a type confusion bug in Chrome's V8 Maglev compiler, was posted on GitHub. Its author says it is not a working exploit.
Test code for CVE-2026-126910, a type confusion bug in Chrome's V8 Maglev compiler, was posted on GitHub. Its author says it is not a working exploit.
Threat actors operating the Qilin ransomware syndicate have breached the University of Texas at Arlington (UTA), compromising campus web servers and exfiltrating confidential administrative records. Independent…
Offensive security researchers have published a functional zero-day local privilege escalation exploit named SignDrop, which circumvents core kernel mitigations within the Windows Common Log File System…
Toronto’s York University has confirmed a major cybersecurity incident that resulted in the unauthorized theft of sensitive personal, medical, and financial records submitted across departmental webforms…
The United Kingdom’s National Cyber Security Centre (NCSC) has officially launched the Cyber Adversary Simulation (CyAS) scheme. The initiative introduces a rigorous government assurance standard to…
WASHINGTON — The Cybersecurity and Infrastructure Security Agency added an actively exploited vulnerability impacting Cisco BroadWorks application servers to its mandatory remediation catalog Wednesday morning. The…
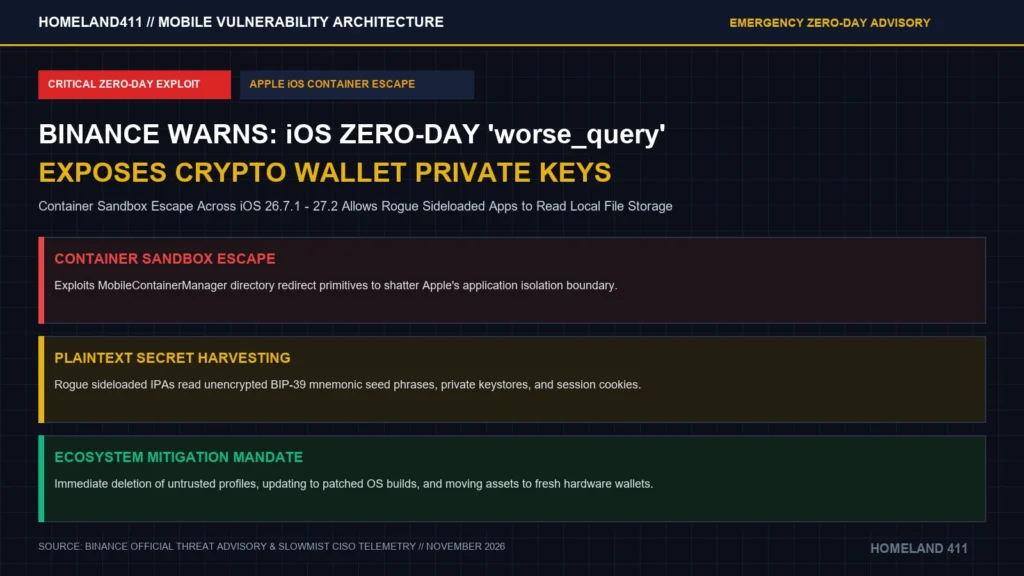
VALLETTA — Digital asset exchange Binance issued an emergency cybersecurity alert Tuesday morning, warning of an unpatched zero-day flaw in Apple iOS software. The flaw allows…
Never Miss An UpdateFollow us on Google News to get our latest security, defense and cyber reporting in your feed. It’s free and takes one tap.
Follow on Google NewsNever Miss An UpdateGet Homeland411 in your Google News feed
Follow