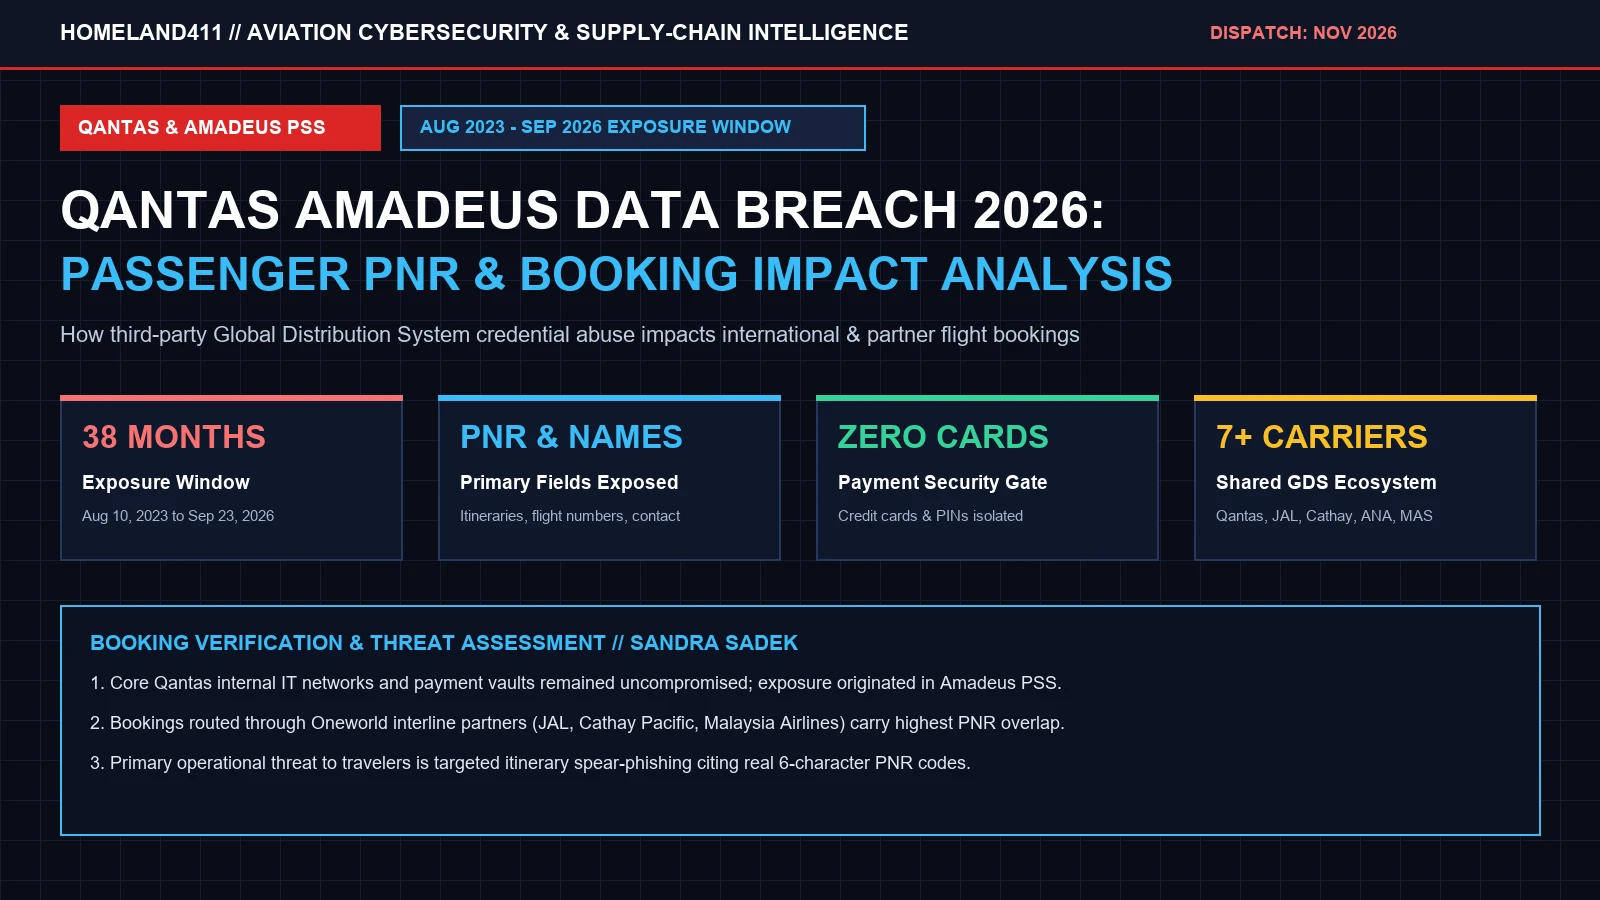
Over 180,000 regional airline reservations have already been confirmed exposed across Asia-Pacific carriers. Now, Qantas Airways is auditing how many Australian bookings were caught in the Amadeus IT Group data breach. Carrier disclosures in late October and November 2026 confirm that intruders abused valid administrative credentials inside Amadeus’s reservation platform. That unauthorized access lasted 38 months between August 10, 2023, and September 23, 2026.
For Qantas passengers, the vendor intrusion compresses two supply-chain compliance risks into one travel window. Qantas confirmed that its internal corporate databases and flight operations remain completely secure. However, the carrier uses Amadeus’s Altéa Passenger Service System (PSS) to synchronize international bookings and alliance ticketing.
Never Miss An UpdateFollow us on Google News to get our latest security, defense and cyber reporting in your feed. It’s free and takes one tap.
Follow on Google NewsTravelers who booked partner routes alongside Malaysia Airlines, Japan Airlines, or Cathay Pacific face immediate exposure of their six-character Passenger Name Record (PNR) codes. In official notices to Australian regulators, Qantas stressed that the intrusion stayed confined to the vendor layer. Both Qantas and Amadeus verified that payment card numbers, bank accounts, and account passwords were never accessed.
How to Check if Your Qantas Booking Was Exposed in the Amadeus Breach
Qantas flyers can verify booking exposure by checking ticket issue dates between August 2023 and September 2026. Passengers should also inspect Oneworld partner flight segments and watch for official carrier email alerts.
Amadeus operates as the primary settlement and reservation engine for international airline alliances. Because of this architecture, booking exposure depends on how a ticket was routed across partner carriers. Even when a flyer buys a ticket on the Qantas website, codeshare legs route that PNR into shared Amadeus partitions.
Three ticketing factors determine whether a Qantas itinerary entered the affected vendor perimeter. First, any reservation created or modified between August 10, 2023, and September 23, 2026 inside Altéa falls within the exposure window. Second, multi-carrier itineraries connecting through Tokyo, Hong Kong, Kuala Lumpur, or Seoul carry the highest PNR overlap. Third, flights booked after September 23, 2026, sit outside the compromised window. Amadeus revoked all stolen credentials before that September cutoff.
| Carrier / Incident Scope | Confirmed Volume & Window | Exposed Reservation Fields | Protected Data & Action |
|---|---|---|---|
| Qantas Bookings | Aug 10, 2023 – Sep 23, 2026 (Audit active) | Full name, 6-char PNR code, flight numbers, dates. | Cards and PINs safe (Qantas Portal →). |
| Cathay Pacific | ~53,000 bookings (Aug 2023 – Sep 2026) | Names, PNR codes, itineraries, select emails. | No passwords exposed (Cathay Notice →). |
| Japan Airlines (JAL) | ~92,000 customers (~2,000 with APIS data) | Names, PNRs, flights; subset of passport IDs. | Direct alerts sent (JAL Advisory →). |
| All Nippon Airways | ~37,800 customers (~1,700 with passport IDs) | Basic itinerary data; small subset of contact info. | Payment cards isolated; email notices sent. |
| Malaysia Airlines & KAL | Aug 2023 – Sep 2026 (Forensic triage active) | PNR booking codes, passenger names, itineraries. | Core airline networks secure; watch for SMS lures. |
| 2025 Qantas CRM Leak | 5.1M – 5.7M profiles (June 2025 incident) | Names, emails, phones, DOBs, Frequent Flyer IDs. | Separate Salesforce breach (OAIC Report →). |
Amadeus PSS vs. the 2025 Qantas Call Center Breach: Key Differences for Travelers
Many Australian travelers confuse the late-2026 Amadeus reservation incident with the standalone breach Qantas disclosed in mid-2025. Both events hit third-party technology suppliers rather than Qantas’s own aircraft or corporate networks. However, the two breaches targeted separate databases and require different security precautions.
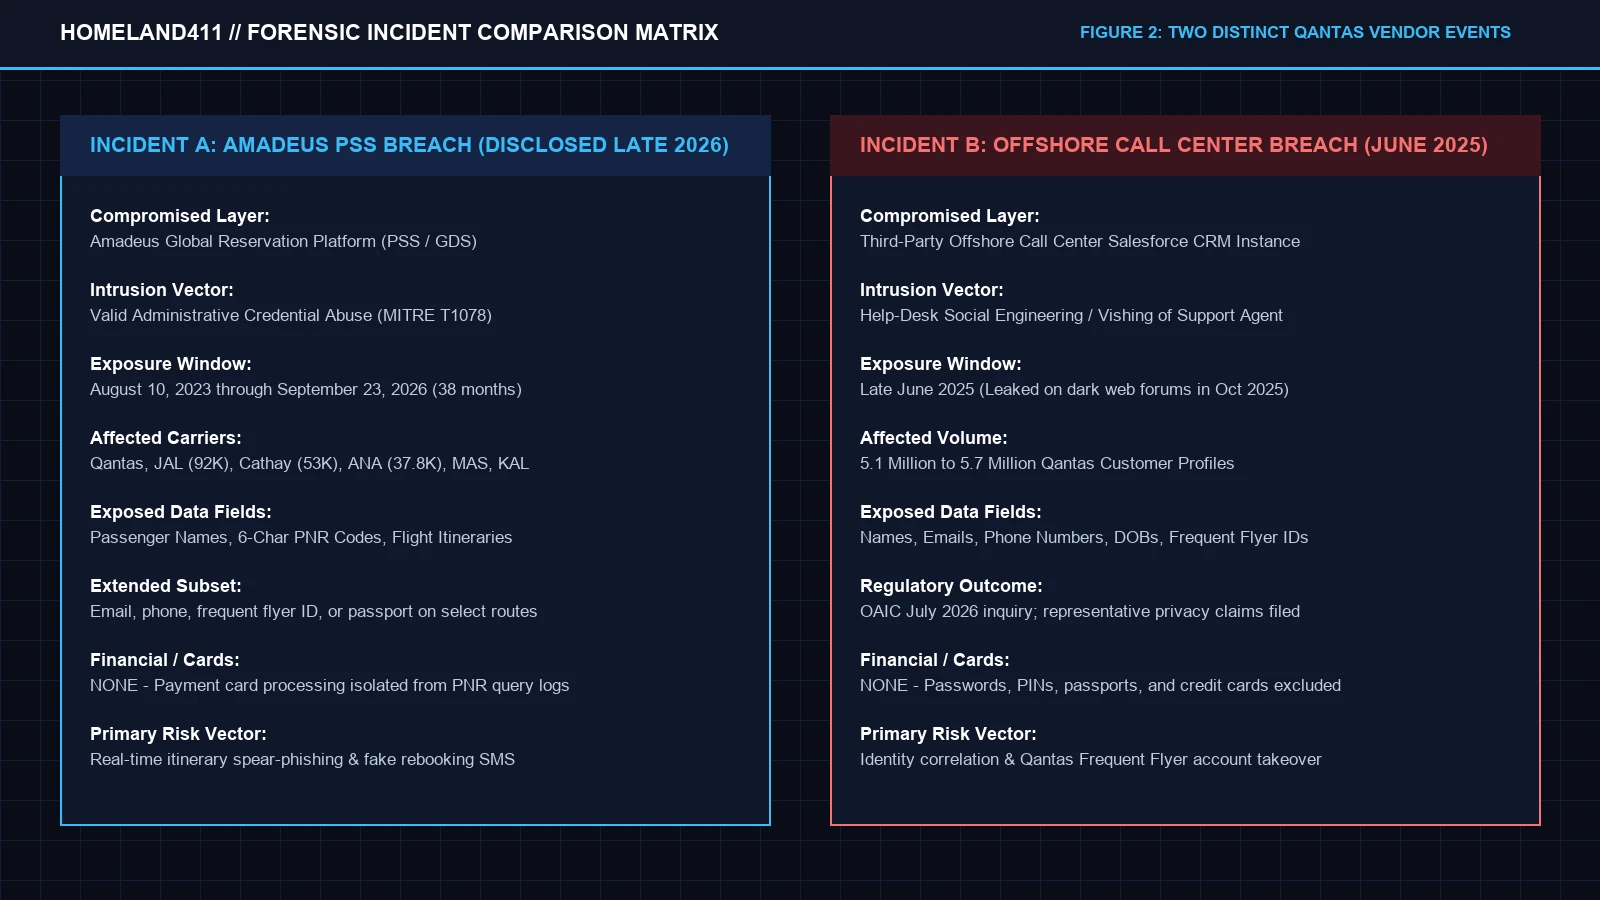
In June 2025, attackers used voice social engineering against an offshore call center agent to breach a Salesforce database. That earlier incident exposed static profile data for roughly 5.7 million Qantas customers. Those stolen records later surfaced on dark web forums in October 2025. By contrast, the 2026 Amadeus event involved valid account credential abuse (MITRE ATT&CK Technique T1078) inside live ticketing systems. This method mirrors the identity-first tradecraft seen in modern enterprise credential intrusions.
Passengers reviewing their personal exposure across both supply-chain events should execute four verification steps immediately:
- Inspect 2023–2026 E-Tickets for Partner Codes: Check confirmation emails for flights booked between August 10, 2023, and September 23, 2026, especially routes including Cathay Pacific (`CX`), Japan Airlines (`JL`), or Malaysia Airlines (`MH`).
- Lock Down Active 6-Character PNR References: An active PNR code paired with a family surname allows anyone to view or modify itineraries on airline portals, so never share boarding passes online.
- Review Passport APIS Exposure on Asian Routes: Roughly 2% to 4% of affected bookings at peer carriers included passport numbers in Advance Passenger Information System (APIS) fields, requiring identity monitoring for trans-Pacific flyers.
- Reject Unsolicited SMS Rebooking Payment Links: Attackers holding real flight numbers and PNR codes send deceptive text alerts demanding card fees for seat changes or disrupted flights.
Why Shared Airline Reservation Systems Remain Prime Targets for Credential Abuse
From an aviation policy perspective, the Amadeus intrusion shows how software consolidation reprices cyber risk across flag carriers. Headquartered in Madrid, Amadeus processes reservations for over 400 international airlines. When a single service account is compromised inside that central hub, the blast radius spans dozens of countries.
Because the attacker authenticated with valid administrative credentials, traditional firewall rules and malware scanners never triggered. The unauthorized queries blended into millions of daily ticketing requests from travel agents and airport gates. Amadeus halted the activity in September 2026 after internal anomaly monitoring flagged unusual query patterns.
“Amadeus contained the unauthorized reservation system access by revoking compromised credentials and enforcing stricter authentication controls. Airline flight operations and payment card vaults remained unaffected throughout the incident.”
— Consolidated Carrier & Amadeus Technical Disclosure Summary, October–November 2026
In July 2026, the Office of the Australian Information Commissioner (OAIC) closed its preliminary inquiry into Qantas’s 2025 call center breach without issuing fines. Regulators noted that Qantas had maintained reasonable preventative vendor controls under existing privacy rules. However, a second vendor exposure within sixteen months outpaces standard compliance tolerances and increases pressure on aviation processors.
Mandatory Security Steps and Upcoming Aviation Privacy Deadlines
For travelers flying in late 2026 and early 2027, the primary danger is itinerary-aware spear-phishing rather than direct bank fraud. Threat advisories from the Australian Cyber Security Centre (ACSC) warn that criminal groups combine older 2025 contact leaks with fresh 2026 Amadeus PNR records. By quoting a passenger’s real flight number and booking code, scammers try to harvest live credit card numbers.
Passengers should verify all flight changes exclusively inside the official Qantas mobile app or on `qantas.com`. Flyers should also rotate their Qantas Frequent Flyer PIN and enable multi-factor authentication on linked email accounts. Tougher enforcement tiers under Australia’s amended Privacy Act take full effect in the Q1 2027 compliance cycle. Those rules subject airlines and reservation vendors to civil penalties reaching $50 million AUD if third-party credential governance fails.