Somewhere above 40,000 files said to have been taken from Eni or from one of its commercial partners were claimed on Friday by the INC Ransom extortion group, which listed the Italian energy company as a data breach victim on its leak site, according to a post by the threat intelligence account Dark Web Intelligence.
The listing was said to refer to “agreements with ENI,” agency contracts and the screening of sub-agents, which led the account to say the data “may come from an Eni commercial agent or partner rather than Eni’s own network,” according to that same post, which noted that Eni had not publicly confirmed an incident.
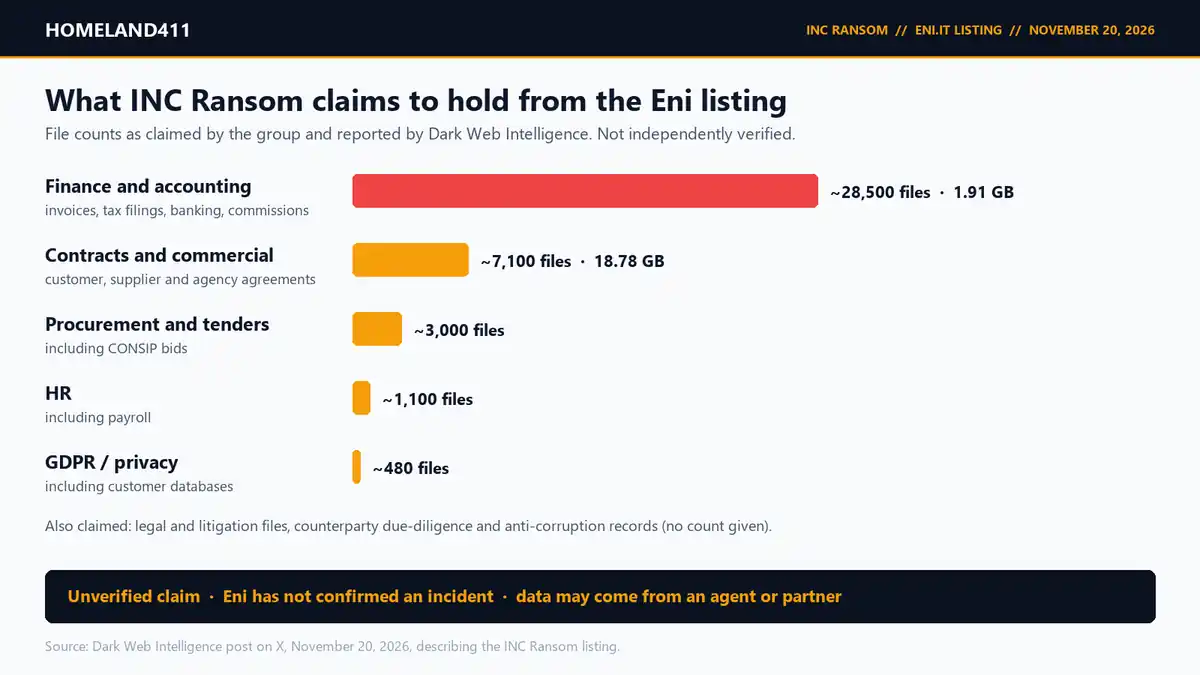
The data was said by the group to include about 7,100 files of contracts and commercial records totaling 18.78 gigabytes, among them customer, supplier and agency agreements, and some 28,500 finance and accounting files of 1.91 gigabytes covering invoices, tax filings, banking and commission records, according to the post.
The rest of the haul was described as about 3,000 public procurement and tender files, including bids made through CONSIP, the Italian state’s central purchasing body, along with legal and litigation files, due-diligence and anti-corruption records, about 1,100 HR files and some 480 privacy files that were said to include payroll and customer databases, according to Dark Web Intelligence.
The listing had not yet shown up in the records kept by the tracking site Ransomware.live when they were checked on Friday morning, and the most recent INC Ransom entries there were dated Thursday, according to the site.
Earlier Eni data breach claims on leak sites
The INC Ransom claim was not the first time the name of the company had turned up on a leak site this year, as an entry for Eni Energy was attributed to a group calling itself Lapsus$ on March 1, according to Ransomware.live.
A listing that paired Eni’s domain with that of Mellitah Oil & Gas, a Libyan company in which Eni holds a stake, was also recorded against the RansomHub group in 2024, according to that same tracker.
Eni itself confirmed in August 2022 that its “internal protection systems have detected unauthorized access to the company network” and said the consequences appeared to be minor, in a statement given to Bloomberg News at the time.
Partner files at issue
The apparent value of the files lay in part in what they could be used for, as procurement, contract and due-diligence records were described in an analyst note on the post as “high-value for tender fraud, invoice scams and targeted phishing” against Eni’s partners and suppliers, according to Dark Web Intelligence, which told readers to treat the listing as “an unverified threat-actor claim.”
The group has been credited with more than 1,050 victims since it began posting them, two of which, listed as AutoZone, Inc. and Chambourcy, were added on Thursday, according to Ransomware.live.
Attacks that reach large companies through their smaller suppliers and agents, the route that the files in this case may reflect, were the subject of a Homeland411 analysis of supply chain security published last month.
This week, a group calling itself AOQIN Leaks claimed 327 gigabytes from the Argentine software firm TopGroup, days after the Qilin gang was linked to a breach at the University of Texas at Arlington, as Homeland411 reported at the time.